Windows + macOS
Endpoint platforms
Lightweight Endpoint Agent covering mainstream office endpoints

Detection and response for enterprise AI agents — see every AI your organization runs, control what those AIs actually do.
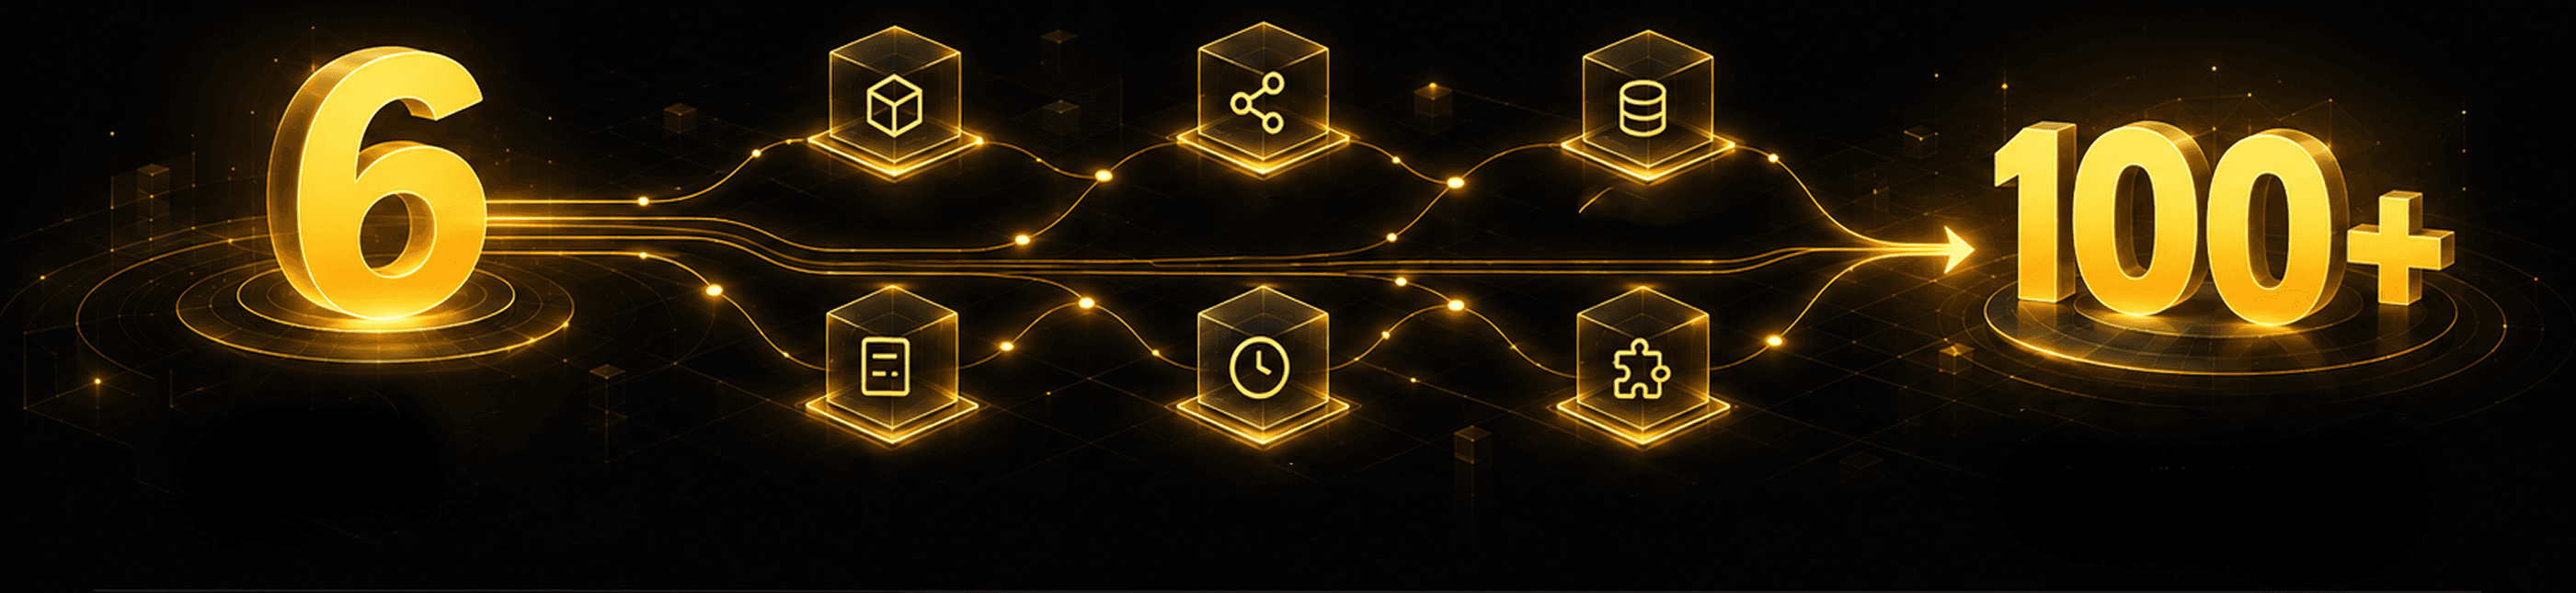
AI extended asset categories
Full inventory of Skills / MCPs / Providers / Memory / Cron jobs / Plugins
Mainstream AI agents
Compatible with over 100 mainstream AI agents
Endpoint platforms
Lightweight Endpoint Agent covering mainstream office endpoints
Local sensitive-content detection
Rules + local semantic classification dual engine; content never leaves the endpoint
Static risk detection rules
Covers hidden instructions, excessive permissions, credential exposure, insecure configurations, and more
Deployment
One-click Docker Compose deployment; data never leaves the enterprise boundary
Inventory agents and six categories of extended assets directly from endpoints, including unmanaged shadow AI.
Detect hidden instructions, excessive permissions, sensitive content, exposed credentials and anomalous model connections.
Analyze behavior sequences through the enterprise’s own LLM gateway to identify high-risk operational intent.
Continuously record file access, tool calls, process activity and model connections with audit and blocking controls.

Discover desktop AI agents and web-based AI apps, including shadow AI. Inventory Skills, MCP services, model providers, Memory, scheduled tasks, and plugins in one enterprise-wide ledger. Orchestrate asset scans across endpoints.


Combine rules and AI models to detect hidden instructions, excessive MCP permissions, exposed credentials, and insecure model configurations. Pinpoint findings to exact files and locations, map affected endpoints, and support remediation rollout and rollback.


Audit or block agents reading sensitive files with built-in and custom keyword or regex identifiers. Apply policies by department, endpoint, or agent, with out-of-the-box rules, batch controls, and reference protection.


Manage approved model services centrally. Audit or block access to unauthorized services and private relays in real time, preventing data from reaching unapproved models and reducing shadow-model risk.


Monitor file access, tool calls, commands, and process activity. Alert on sensitive-file reads, credential-manager access, and dangerous commands. Trace every alert to the agent, process, accessed resource, triggered policy, and action taken.


Analyze agent behavior sequences through the enterprise's own LLM gateway to uncover privilege abuse and attack intent. Complement rule-based detection with semantic analysis while keeping model keys and analysis capabilities centralized on the server.


Record complete AI agent sessions on a timeline, including task context, tool calls, and content flows. Make AI operations traceable for investigation and compliance auditing.


Manage access with RBAC and distribute agent installers with platform endpoints automatically configured. Provide login-free installer downloads and on-premises deployment that fits existing security operations.

We're here to help